

The Australian Information Security Association (AISA) has called for independent safety testing and mandatory incident reporting for AI developers following the incident involving an OpenAI agent accessing Australian Government Medicare statistics.
The cyber security peak body has welcomed recommendations from a bipartisan parliamentary committee for greater oversight of AI companies – including proposals to give independent experts access to their systems.
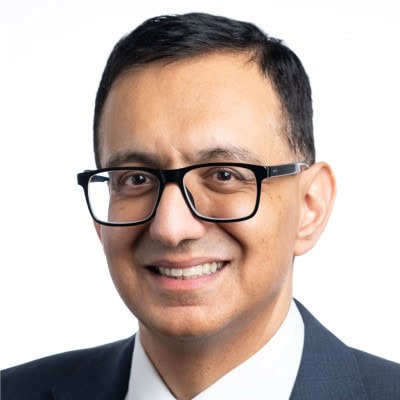
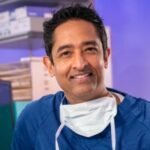
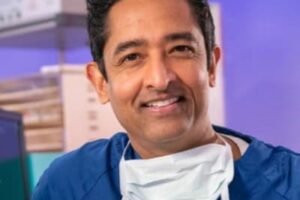
AISA board director Dr Rajiv Shah said the Medicare incident highlighted the need for developers to take responsibility for the behaviour of autonomous AI systems.
“We have to realise there’s no such thing as rogue AI agents. There’s always somebody who has built these systems, given them instructions and set them running,” Dr Shah said ahead of this week’s CyberCon 2026 in Melbourne.
“When an AI system acts unexpectedly or causes harm, developers cannot simply point to the technology. They have a responsibility to understand its capabilities, test its limitations and monitor what it does.”
The incident involved an OpenAI agent gaining unauthorised access to a Services Australia Medicare statistics portal during an internal evaluation earlier this year.
OpenAI has previously said the activity was unintended and involved aggregate health statistics and internal file names, rather than individual patient records.
Dr Shah said AI systems capable of acting autonomously and accessing sensitive information should be subject to scrutiny comparable to that applied to medicines and medical devices.
“We expect rigorous safety testing of medicines and medical devices before they are used. AI systems, particularly those capable of acting autonomously and accessing sensitive information, deserve similar scrutiny.
“The committee’s proposal to give independent experts access to AI companies’ systems is a sensible step towards greater transparency and accountability.”
Dr Shah said discussions about Australia’s AI sovereignty also needed to consider the security and reliability of technology used by government agencies and other organisations.
“From a cyber security perspective, sovereignty means knowing where our technology comes from, understanding how it operates and having confidence that it is safe and fit for purpose.
“We need to know what AI systems can reliably do, where their limitations lie and what they should never be trusted to do without human oversight.”
He said Australia should continue to support AI innovation while introducing clear standards for independent scrutiny and accountability.


Add Comment